Your Operating System you are using to access your NAS.
Win11
NAS model
TS-253A
Firmware Version/Build numbers - not just “The latest”
QTS 5.2.10.3568 Build 20260722
Network Setup (ie Single Port or Port Trunking)
Single port
Hello,
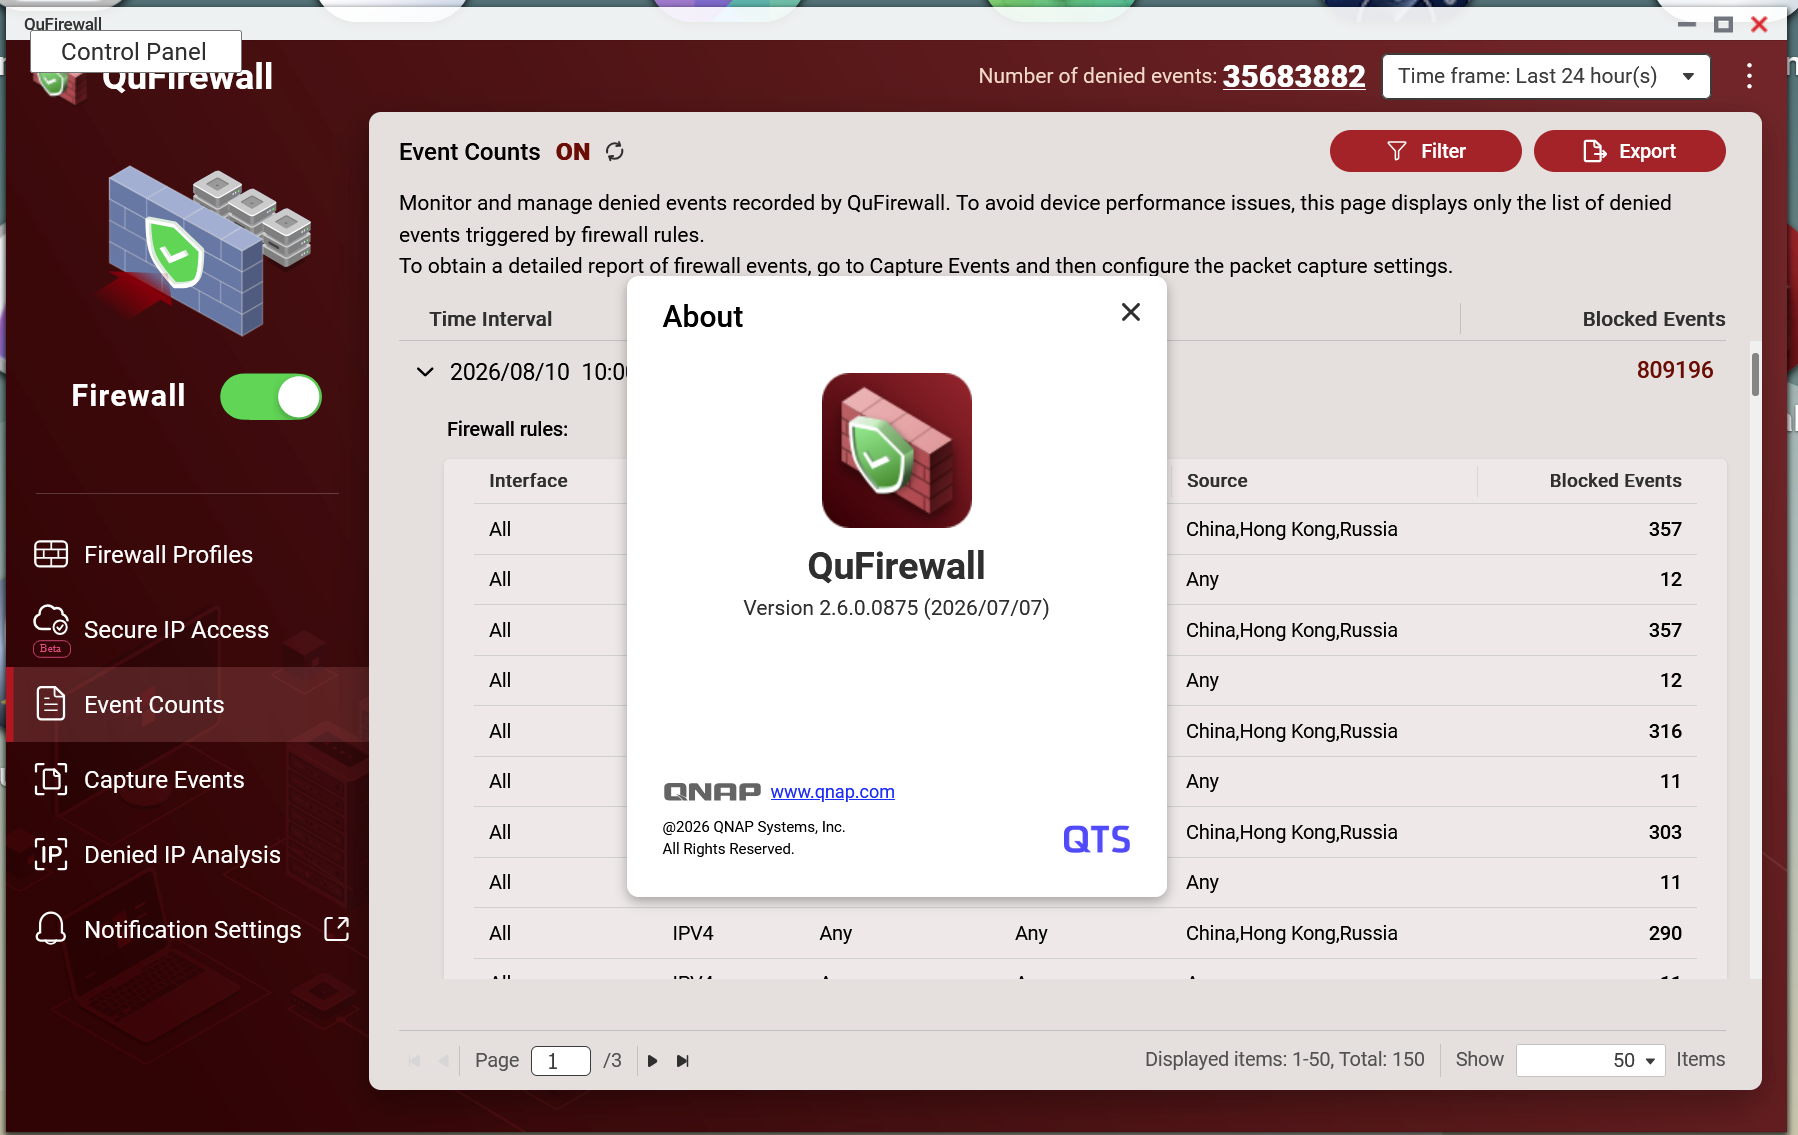
I have a dilemma with the new version of QU Firewall 2.6.0. as now it is creating 10 times more blocked events than before.
I have a basic firewall profile to only allow certain ports from certain regions of the world and before the version 2.6.0, (2.5.0) it was blocking about 30.000 to 60.000 events per day which for me sounds reasonable.
Now the new version has a bug from my perspective as it is logging 35 milion events per 24 hours and the blocked rules that it is applying to is in some cases logged 10 times in the same row.
For example blocking TOR, or blocking a country.
Then in the next lime I have the same rule applying with blocking the above rule.
It is like the rules are applying over and over after blocking one IP then they go to the top and apply again.
Qnap said that they’ve confirmed there’s a (count) problem, yet we’ve heard nothing further, apart from it being fixed in a further update.
Being so, why-o-why (until that unknown date), can’t they roll back the previous (proper working) release, or at least let us know where we can download it.
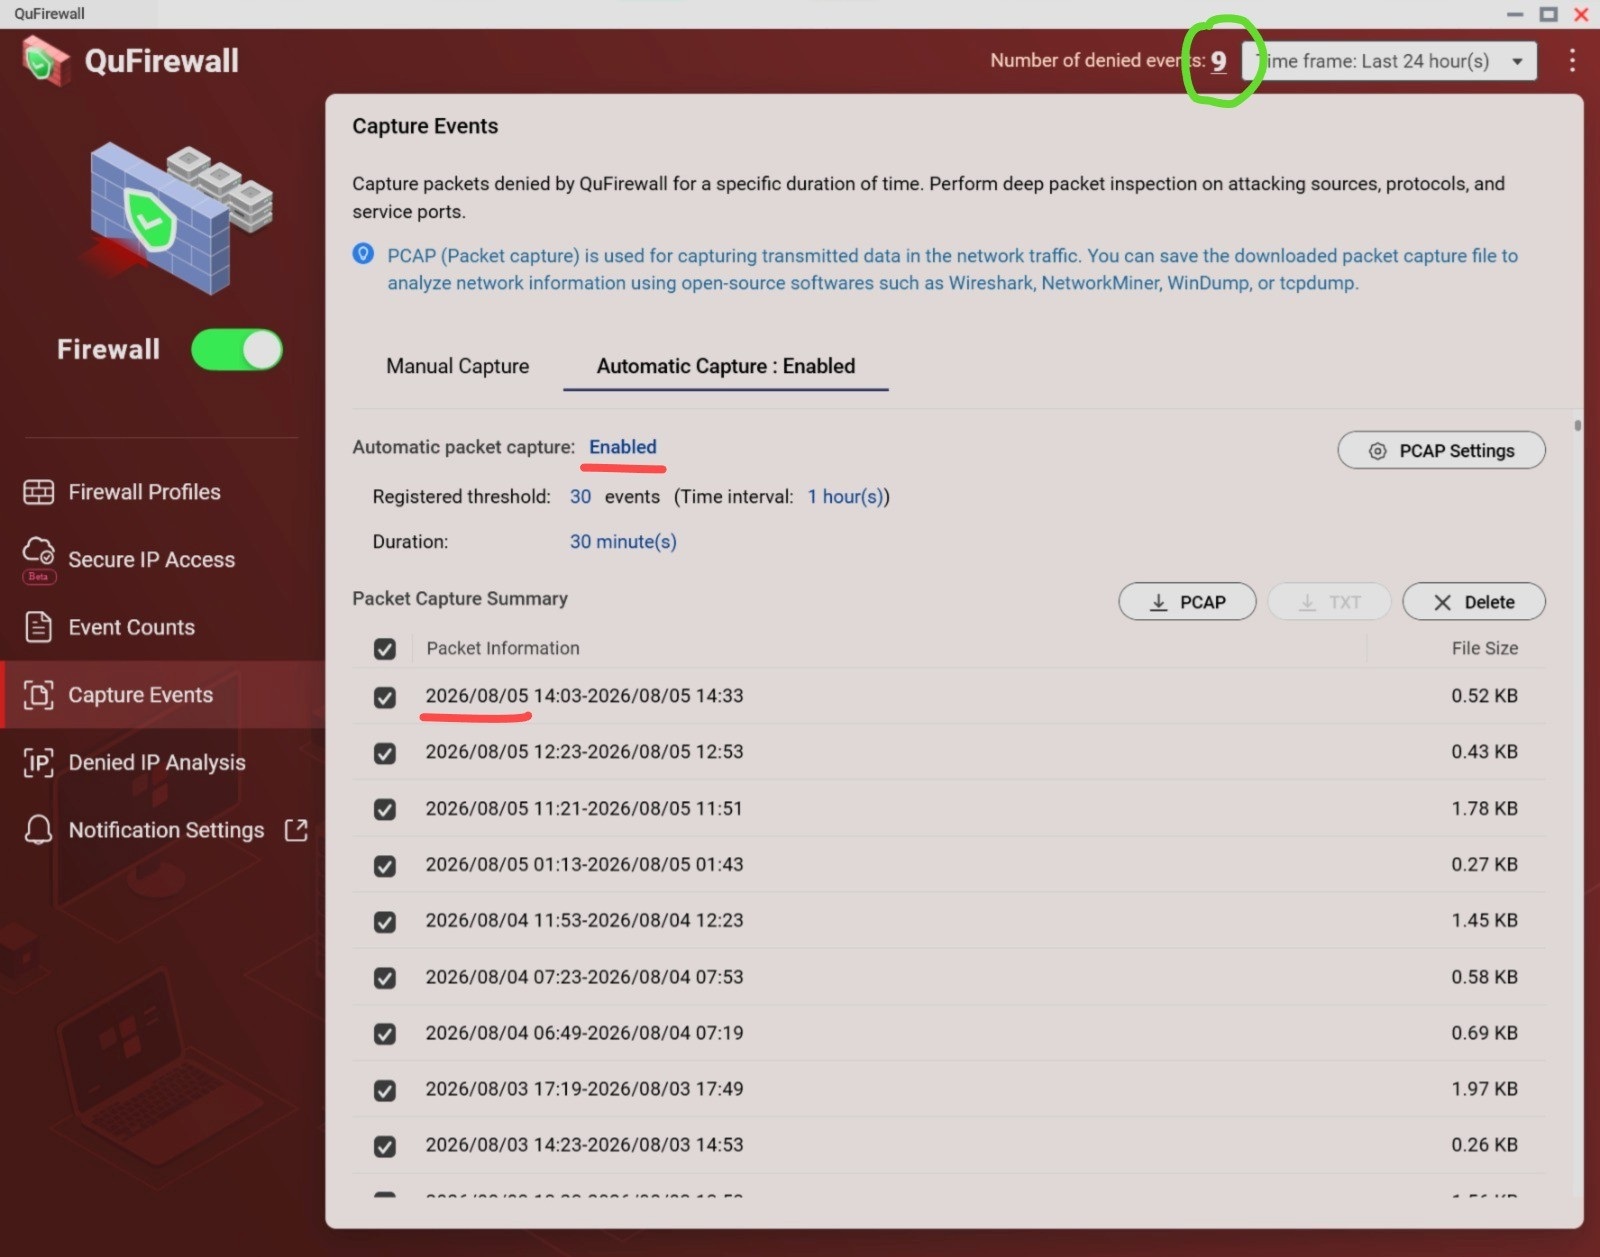
The last automatic packet captured event for me was on the 5th August which was the day of this latest update.
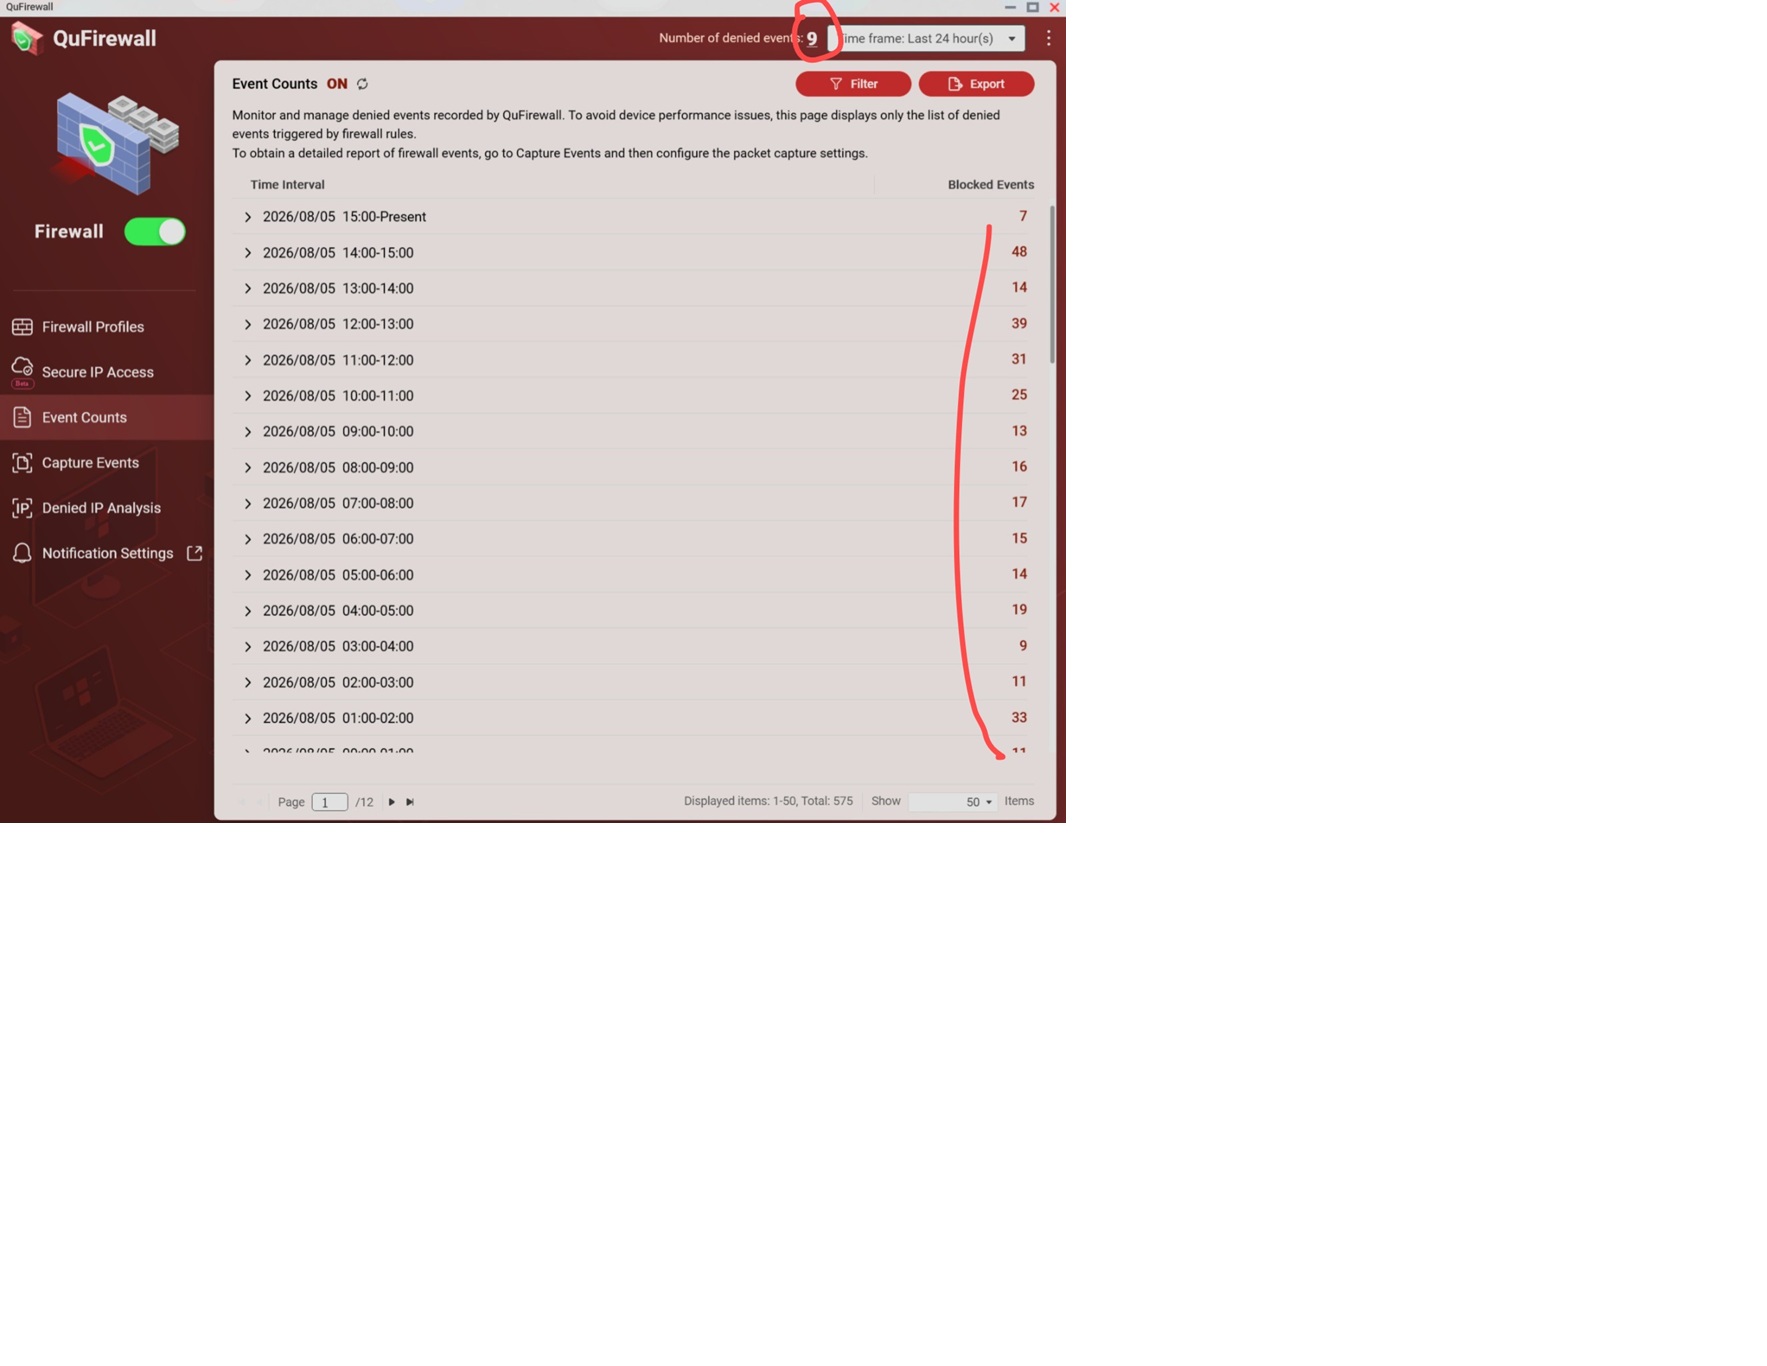
My number of denied events has not changed from 9 since the latest release date.
We’re sorry for the inconvenience. We’ve confirmed internally that version 2.6.0 can cause this issue under certain conditions. We will be removing this version and will fix the issue in a future release. Thank you for your understanding.
Root cause:
This is a known regression in QuFirewall 2.6.0.x — a denied-event counter / interval-rollover issue:
* The denied-event aggregation window becomes frozen on a single stale interval and never rolls forward, so the same events are re-counted repeatedly (roughly once per minute). This inflates the “denied events” number shown in the overview.
* Those inflated counts are phantom — not backed by real captured packets. Denied IP Analysis correctly shows ~0 real packets, so Automatic Capture, Manual Capture, and Denied IP Analysis appear “empty.”
In other words, PCAP capture is not actually missing or malfunctioning — the underlying event-counting/logging pipeline in 2.6.0.0875 is defective, which both fabricates the high denied-event numbers and leaves captures/analysis empty. Because the events are phantom, there is no actual unlogged malicious traffic, so this is not a real security exposure.
You may check in QuFirewall > Denied IP Analysis, if there are IPs denied, or in QuLog Center > Event Log if there are failed connection attempts from unauthorized IPs/client devices.
Regarding the fix version, I am waiting for our Dev Team for feedback if any ETA release.