Model TS-653D
Firmware QTS 5.2.10.3577
QuFirewall Version 2.5.0 (2025/11/10)
Container Station
Version 3.1.2.1742 (2025/11/26)
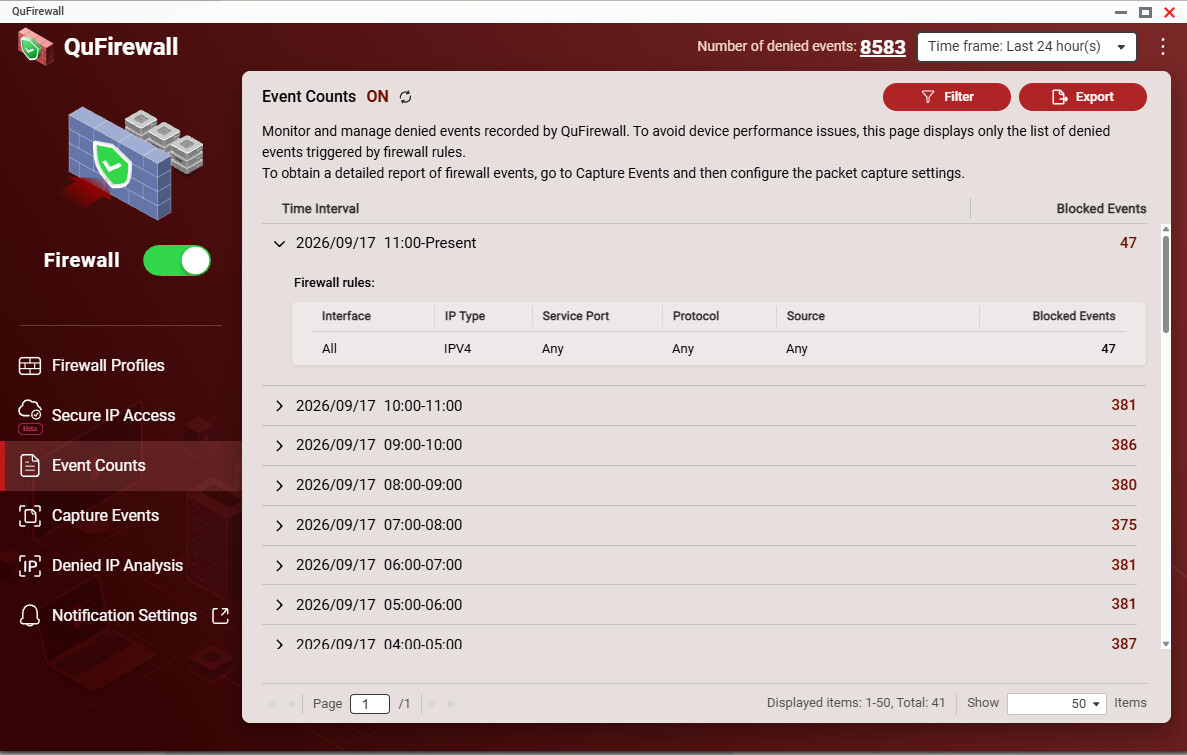
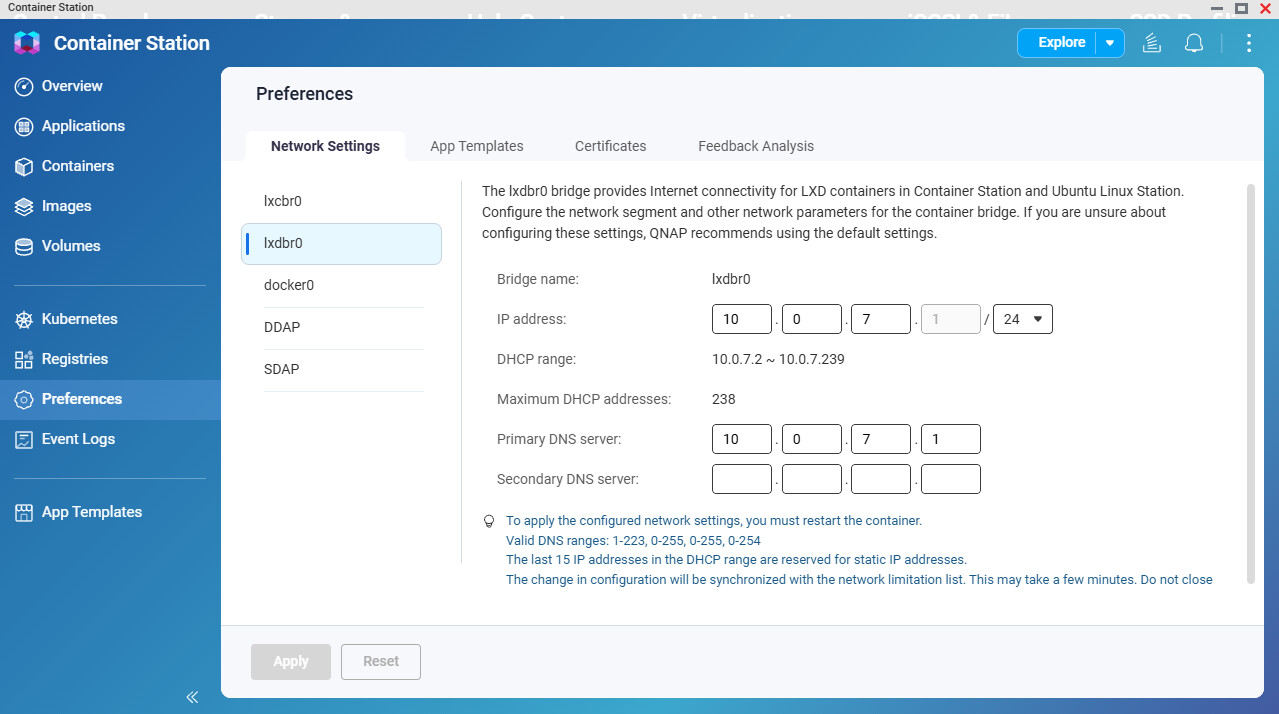
So I recently looked at the QuFirewall, and noticed I keep getting “denied events”. When looking at them it doesn’t really explain it well. So I did a packet capture and noticed all the denies were coming from a source address of 10.0.7.1 which is the lxdbr0 bridge interface, which is the interface for LXD containers and I am not running any of those.
Here is a snip of the packet capture. I got basically around 30ish of these entries over a 5 min period.
Sep 17 11:12:50 NAS RULE=27 ACT=DROP IN=lxdbr0 OUT= MAC=45:00:00:44:52:cb:40:00:ff:11:36:e1:0a:00 SRC=10.0.7.1 DST=224.0.0.251 LEN=68 TOS=00 PREC=0x00 TTL=255 ID=21195 DF PROTO=UDP SPT=5353 DPT=5353 LEN=48 MARK=10000

Sep 17 11:13:15 NAS RULE=27 ACT=DROP IN=lxdbr0 OUT= MAC=45:00:00:4e:af:a5:40:00:40:11:67:fa:0a:00 SRC=10.0.7.1 DST=10.0.7.255 LEN=78 TOS=00 PREC=0x00 TTL=64 ID=44965 DF PROTO=UDP SPT=137 DPT=137 LEN=58 MARK=10000
I am running the basic firewall profile with everything left at the default settings.